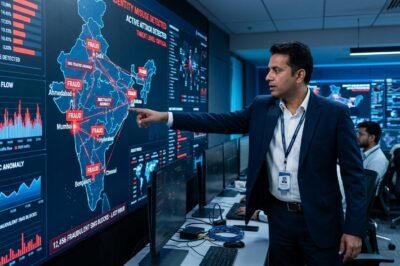
In an era where digital connectivity defines the fabric of commercial interaction, the sanctity of corporate identity has become a primary battleground for cybersecurity and regulatory compliance. The recent news regarding a case filed against three telemarketing firms for allegedly misusing the SMS identities of established companies highlights a systemic vulnerability in the global telecom ecosystem. For years, the convenience of Short Message Service (SMS) has been leveraged by corporations to provide two-factor authentication, delivery updates, and promotional offers. However, this convenience rests entirely on the pillars of trust and sender verification. When that trust is breached through the unauthorized use of ‘headers’—the unique identifiers that appear at the top of a text message—the entire digital infrastructure of a nation is put at risk. This development, as reported by NDTV, serves as a stark reminder that as digital defenses become more sophisticated, the methods employed by bad actors to bypass them are equally evolving. The psychological impact of receiving a message from what appears to be a ‘trusted’ source like a bank or a major e-commerce platform cannot be overstated, as it bypasses the typical skepticism users apply to unknown numbers. This incident is not merely a localized regulatory breach but a symptom of a deeper crisis in how digital identities are managed and authenticated in the high-frequency world of mass telemarketing.
The Mechanics of Header Misuse and Identity Hijacking
To understand the gravity of the case against these three telemarketing firms, one must first understand the technical architecture of enterprise messaging. In India and many other jurisdictions, companies are assigned specific six-character alpha-numeric strings known as ‘Headers’ or ‘Sender IDs.’ These headers, such as ‘HDFCBK’ for HDFC Bank or ‘AMAZN’ for Amazon, are meant to be unique to the entity. Under the current Distributed Ledger Technology (DLT) framework implemented by the Telecom Regulatory Authority of India (TRAI), these headers must be registered on a blockchain-based platform to prevent spoofing and unauthorized usage. However, the case reported by NDTV suggests that certain telemarketing entities found ways to manipulate these registrations or exploit loopholes in the verification process to send messages using headers that did not belong to them.
This misuse typically involves a process where a telemarketer, who has access to the bulk SMS gateway, misrepresents their client’s identity or uses a dormant header registered by another company to push content. The technical complexity of these gateways often allows for a ‘spoofing’ effect where the metadata of the SMS packet is altered before it reaches the carrier’s delivery center. For the end consumer, the message appears in the same thread as legitimate communications from the actual company, making it nearly impossible to distinguish between a genuine update and a fraudulent or unsolicited promotion. This breach of protocol doesn’t just annoy users; it creates a direct channel for smishing (SMS phishing) attacks, where users are lured into clicking malicious links under the guise of an urgent corporate notification.
Regulatory Framework and the Failure of TCCCPR 2018
The Telecom Commercial Communications Customer Preference Regulations (TCCCPR), 2018, was supposed to be the definitive solution to the menace of unsolicited commercial communications (UCC). By introducing DLT, the regulator aimed to create a transparent, immutable record of every header and message template. The current legal action against the three firms indicates a significant breakdown in the enforcement or the technical integrity of this system. According to reports, the firms are accused of violating various sections of the Information Technology Act and the Indian Penal Code, specifically those related to personation and cheating by using computer resources.
Statistically, the volume of SMS traffic in India is staggering, with billions of messages sent monthly. This sheer scale makes manual monitoring impossible. Regulatory experts point out that the DLT system, while robust on paper, relies heavily on the ‘Principle Entities’ (the companies) and the ‘Telemarketers’ (the firms) to act in good faith. When telemarketers prioritize volume and client acquisition over compliance, the system’s safeguards are circumvented. The case highlights that even with blockchain-based tracking, the human element—specifically the verification of the relationship between a telemarketer and the brand they claim to represent—remains a critical point of failure. If a telemarketer can register a header by providing forged authorization letters, the technological solution becomes moot.
The Deep Impact on Corporate Brand Integrity and Consumer Trust
For a corporation, its SMS header is more than just a delivery tag; it is a digital signature. When third-party telemarketers misuse these signatures, the brand equity of the targeted company is immediately compromised.
- Erosion of Trust: Customers who receive spam or fraudulent links from a trusted header lose confidence in that brand’s ability to protect its communication channels.
- Financial Liability: If a customer is defrauded through a misused header, the company whose identity was stolen may face legal challenges and demands for compensation, even if they were not the ones who sent the message.
- Operational Overhead: Companies must spend significant resources on public relations and customer support to clarify that the messages were not authorized, diverting funds from productive business activities.
Furthermore, the broader impact on the digital economy is profound. If consumers stop trusting SMS as a communication medium, the efficiency of transactional updates—such as OTPs for banking—declines. This leads to a higher rate of abandoned transactions and a slowdown in digital commerce. The NDTV report underscores that the misuse by these three firms isn’t just an administrative lapse; it is an assault on the reliability of the entire mobile-first ecosystem that India has built over the last decade.
Legal Repercussions and the Specifics of the NDTV Investigation
The investigation into these three firms is expected to set a precedent for how telemarketing fraud is handled in the future. Reports suggest that the authorities are looking into the financial trails between the clients who commissioned the messages and the telemarketers who executed the campaigns. Under Indian law, the unauthorized use of a company’s identity can lead to charges of forgery, criminal breach of trust, and violations of the IT Act 2000. Specifically, Section 66D, which deals with punishment for cheating by personation by using computer resources, could be invoked, carrying a penalty of imprisonment and heavy fines.
The specific firms involved, while not all named in initial press releases, are being scrutinized for their internal logs. Investigators are examining the ‘scrubbing’ process—the phase where messages are checked against a database of ‘Do Not Disturb’ (DND) numbers and registered templates. If it is found that these firms bypassed the scrubbing process or used unapproved templates under stolen headers, the legal consequences will likely include the permanent blacklisting of these entities from the telecom sector. This move would send a clear signal to the thousands of other telemarketing agencies that regulatory compliance is non-negotiable.
The Path Forward: Technological Countermeasures and AI Integration
As the legal case unfolds, the industry is looking toward more advanced technological solutions to prevent a recurrence. The current DLT system is being augmented with Artificial Intelligence (AI) and Machine Learning (ML) filters. These AI tools are designed to detect anomalous patterns in SMS traffic. For example, if a header traditionally used for transactional banking messages suddenly starts sending promotional content for high-interest loans or gambling, the system can automatically flag and block the traffic in real-time. The integration of AI into the telecom core is no longer a luxury but a necessity for national security.
Moreover, there is a push for a ‘Zero-Trust’ model in SMS delivery. In this model, every single message packet would require a cryptographic signature that links back to a verified, hardware-secured key held by the principal entity. This would effectively eliminate the possibility of header spoofing, as the telemarketer would never possess the private key required to sign the message on behalf of the company. While this adds a layer of latency and cost, the protection it offers against identity theft is unparalleled. The industry is also discussing the implementation of ‘Verified SMS’ features, similar to verified social media accounts, where the mobile operating system displays the company’s logo and a checkmark only if the message passes a rigorous multi-factor authentication check at the carrier level.
Conclusion on Future Implications: A Necessary Reckoning
The case against the three telemarketing firms marks a turning point in the regulation of digital communications. It signals the end of the era of ‘wild west’ telemarketing where entities could hide behind the complexity of the telecom grid to conduct unauthorized activities. Moving forward, we can expect a much tighter regulatory environment. The Telecom Regulatory Authority of India is likely to introduce stricter KYC (Know Your Customer) norms for telemarketers, treating them with the same level of scrutiny as financial institutions. This incident will also force companies to take a more proactive role in monitoring their own digital identities, perhaps employing third-party cybersecurity firms to ‘audit’ the SMS gateways and ensure their headers are not being exploited.
Ultimately, the resolution of this case will define the safety of the digital experience for millions of mobile users. As we transition further into a digital-first society, the protection of our digital identities—and the identities of the institutions we trust—must be paramount. The legal action reported by NDTV is not just about punishing three firms; it is about reinforcing the integrity of the communication channels that power the modern world. If the regulators succeed in making an example of these entities, it will pave the way for a more secure, transparent, and trustworthy digital future for all stakeholders involved.
Leave a Reply